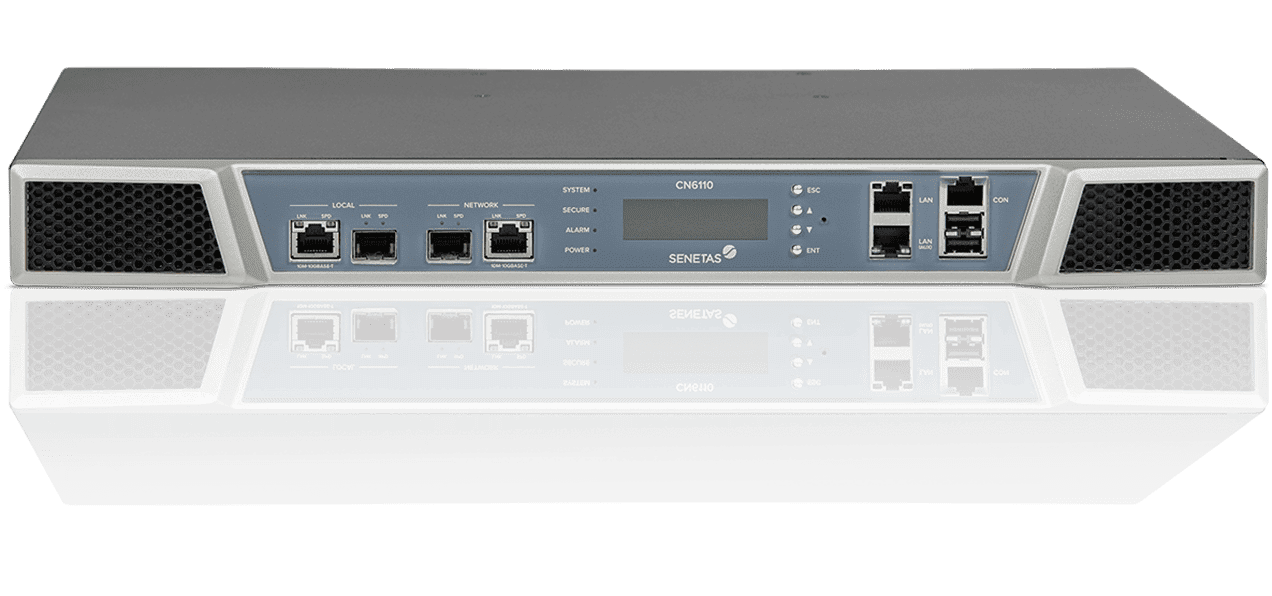
CN6110 Network Encryptor
Quantum-Ready, Carrier-Grade Encryption at 1 and 10Gbps
The problem it solves
Data crossing metro and wide-area networks is vulnerable to interception, breaches, and the emerging “Harvest Now, Decrypt Later” quantum threat.
Traditional security often forces a trade-off: protect the data and slow the network, or keep performance and accept risk. The CN6000 Series removes that trade-off — encrypting data in motion at full line rate, with near-zero latency and no disruption to your network.
Who is it for?
Governments, defence, critical infrastructure, financial services and healthcare organisations that move business-critical data at 1/10Gbps and need certified, sovereign-grade protection they can deploy and forget.
Family key features

Certified high assurance
Common Criteria, FIPS 140-3 Level 3 and NATO — purpose-built for government and defence.

Full line-rate, near-zero latency
FPGA cut-through encryption with no measurable impact on the network.

Network independent
Concurrent, policy-based encryption across Layers 2, 3 and 4 and any topology — point-to-point, hub & spoke or mesh.

Crypto-agile and quantum-ready
In-field, firmware-based algorithm upgrades, including NIST PQC and sovereign algorithms.

Set-and-forget key management
Intrinsic, zero-touch, self-healing key generation — no reliance on external key servers.

Flexible and scalable
Single or multi-port, 1Gbps to 4×10Gbps, with scalable licensing.
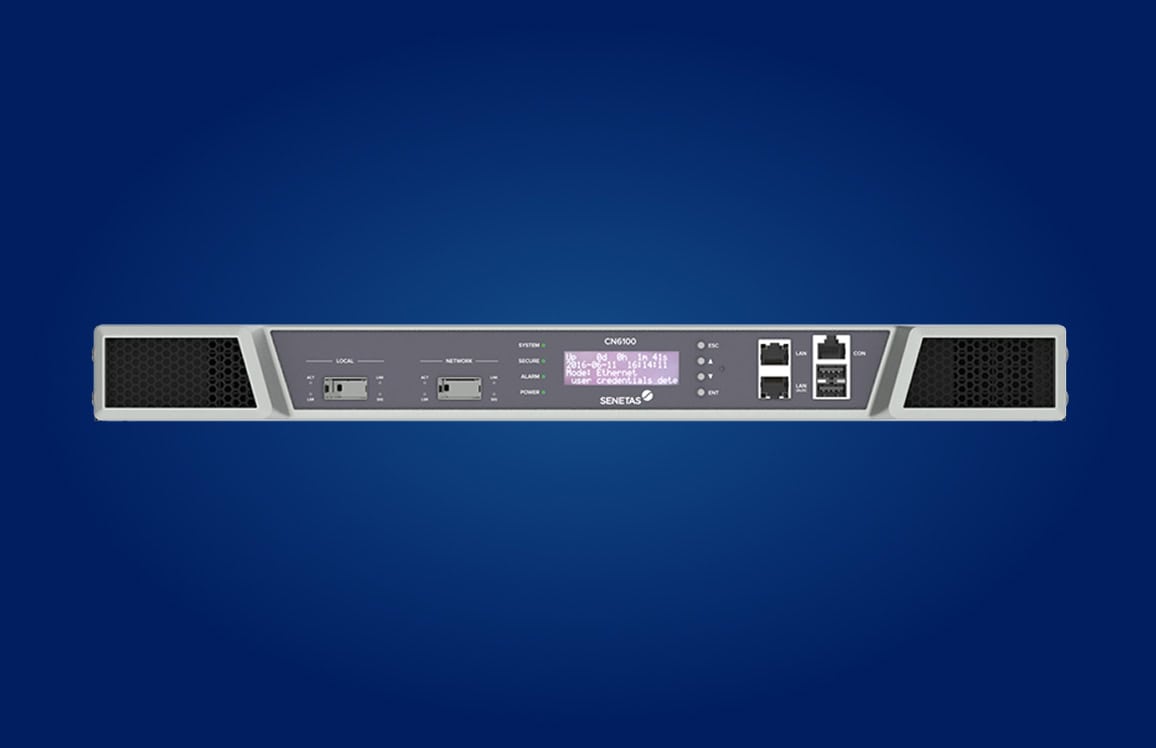
Moving on from the CN6100?
The CN6100 is now end-of-life, with full support continuing until 31 December 2026.
The CN6110 is its direct replacement — quantum-ready, with 1/10Gbps ports in a slimline chassis, and fully interoperable with your existing
CN Series deployment.
The line-up
One platform, three ways to deploy — fully interoperable across the CN Series.
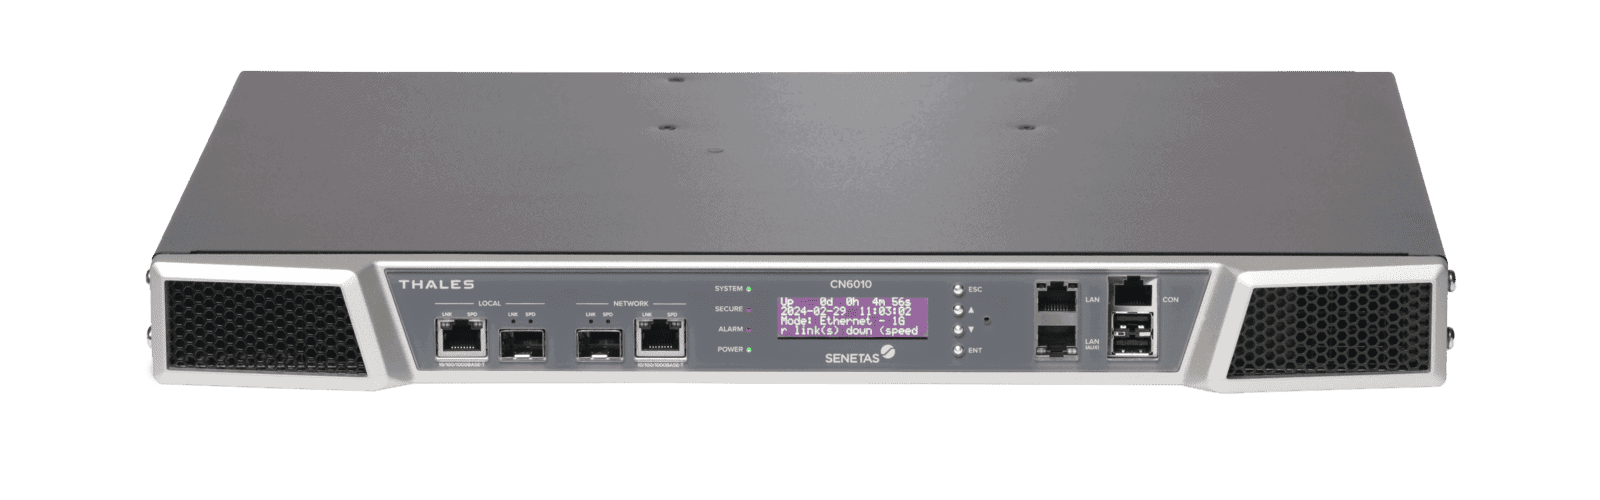
CN6010
Certified 1Gbps encryption in a compact 1U.
The entry point to the CN6000 platform. The CN6010 delivers full line-rate, defence-grade Layer 2, 3 and 4 encryption at 1Gbps — with the same certifications and crypto-agility as the rest of the range. Ideal for branch, edge and “encrypt everywhere” rollouts where budget and rack space matter.
1Gbps full-duplex
Full line-rate encryption with under 10µs latency.
Certified high-assurance
Common Criteria, FIPS 140-3 Level 3 and NATO.
Flexible interfaces
RJ45 and SFP in a single 1U appliance.
Crypto-agile
In-field firmware upgrades, quantum-ready.
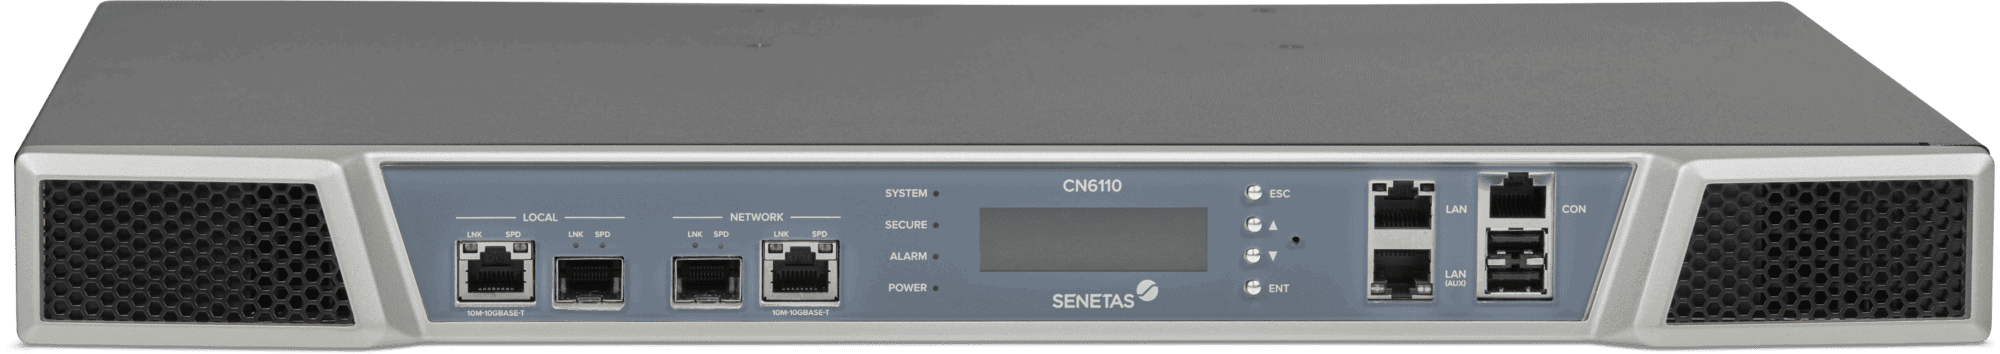
CN6110 (NEW)
Quantum-ready 1-10Gbps encryption.
The next-generation successor to the CN6100: 1/10Gbps in a new slimline chassis. Configured without an IP address on its data ports, the CN6110 stays invisible to attackers — removing the encryptor from the discoverable network entirely.
Fully crypto-agile and upgradeable to quantum-safe algorithms in firmware, it protects your data today and your hardware budget for the next decade.
The workhorse you can plug in and forget — a micro “bump in the wire” that quietly assures every packet reaches its destination, encrypted.
Dual 1/10Gbps
Both speeds in one slimline unit, with two SFP+ transceivers.
Transport Independent Mode
Tunnel-free encryption across Layers 2, 3 and 4 - no architectural change.
Invisible attack surface
No routable IP on data ports - the encryptor isn’t discoverable on the network.
Quantum-ready and crypto-agile
Firmware-upgradeable to quantum-safe and sovereign algorithms.
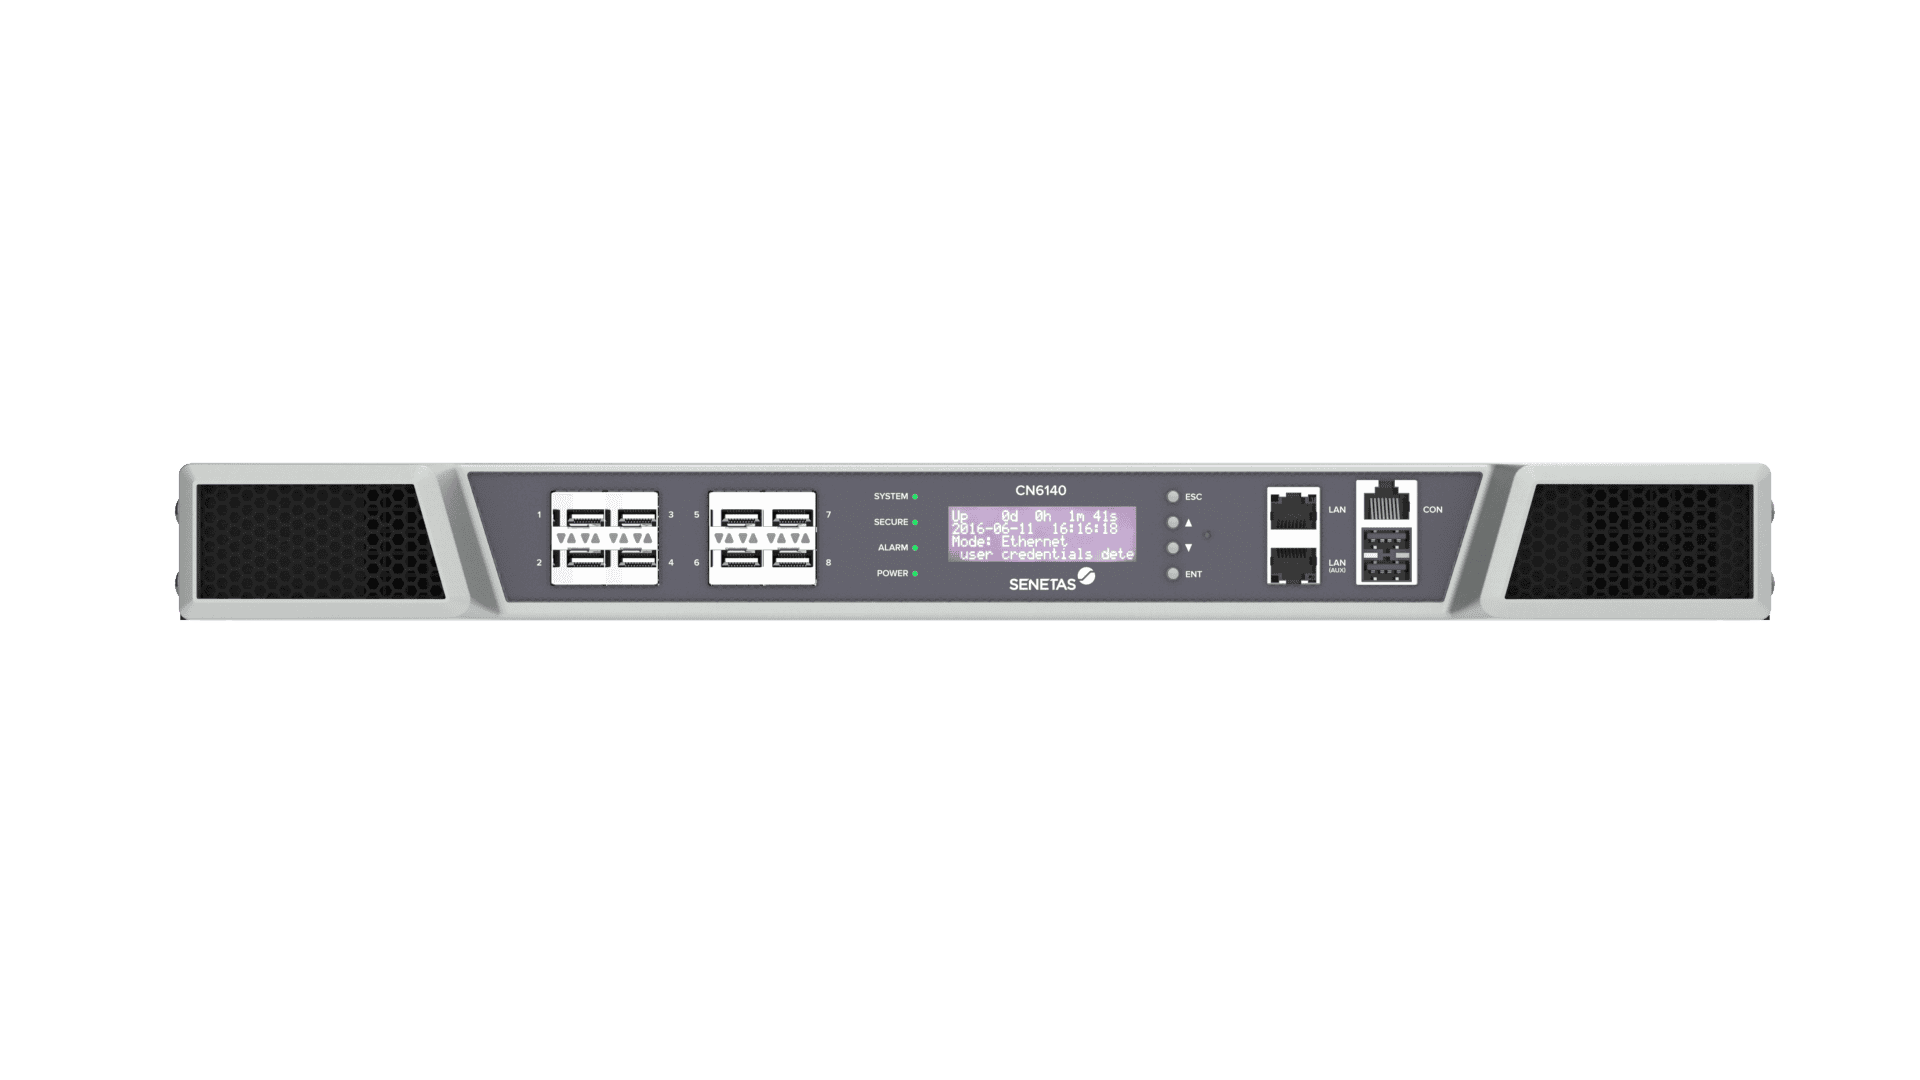
CN6140
Scalable single or multi-port encryption, up to 4×10Gbps.
The flexible flagship of the CN6000 Series. Available as a single-port or multi-port device with per-channel rate limiting, so you can tailor encryption from 1Gbps up to 4×10Gbps in one 1U appliance — consolidating multiple links into a single certified platform.
Up to 4×10Gbps
Four encryption channels in a single 1U unit.
Single or multi-port
Per-channel rate limiting from 1Gbps to 4×10Gbps.
Certified high-assurance
Common Criteria, FIPS 140-3 Level 3 and NATO.
Ultra-low latency
Under 5µs at 10Gbps.
| Feature | CN6010 | CN6140 Single Port | CN6140 Multi-Port | CN6110 (NEW) |
|---|---|---|---|---|
| Physical encryption channels | 1 | 1 | Up to 4 | 1 |
| Maximum Speed | 1Gbps | 10Gbps | 4 × 10Gbps | Up to 10Gbps |
| Dual 1G / 10G capability | – | – | – | ✓ |
| Ethernet point-to-point, hub & spoke, mesh full-duplex encryption | ✓ | ✓ | ✓ | ✓ |
| Protocol and application transparent | ✓ | ✓ | ✓ | ✓ |
| Common Criteria EAL4+ certified | ✓ | ✓ | ✓ | Status to be confirmed |
| FIPS 140-3 Level 3 certified | ✓ | ✓ | ✓ | Certification in progress |
| Low overhead full duplex line-rate encryption | ✓ | ✓ | ✓ | ✓ |
| Front panel access for all interfaces | ✓ | ✓ | ✓ | ✓ |
| Ultra low latency for high performance | ✓ | ✓ | ✓ | ✓ |
| Support for external (X.509v3) CAs | ✓ | ✓ | ✓ | ✓ |
| Robust AES encryption algorithm | ✓ | ✓ | ✓ | ✓ |
| CRL and OCSP server support | ✓ | ✓ | ✓ | ✓ |
| Automatic key management | ✓ | ✓ | ✓ | ✓ |
| Flexible encryption policy engine | ✓ | ✓ | ✓ | ✓ |
| Encrypts Unicast, Multicast and Broadcast traffic | ✓ | ✓ | ✓ | ✓ |
| Network interfaces | RJ45, SFP | SFP, SFP+ | SFP, SFP+ | RJ45, SFP+ |
| Policy based on MAC address or VLAN ID | ✓ | ✓ | ✓ | ✓ |
| Support for Jumbo frames | ✓ | ✓ | ✓ | ✓ |
| Self healing key management in the event of network outages | ✓ | ✓ | ✓ | ✓ |
| Per packet confidentiality and integrity with AES-GCM encryption | ✓ | ✓ | @1Gbps only | ✓ |
| Automatic network discovery and connection establishment | ✓ | ✓ | ✓ | ✓ |
| Reduced attack exposure (data ports configurable without an IP address) | – | – | – | ✓ |
| Centralised configuration and management using CM7 and SNMPv3 | ✓ | ✓ | ✓ | ✓ |
| AES 128 or 256 bit keys | 128/256 | 128/256 | 128/256 | 128/256 |
| Remote management using SNMPv3 (in-band and out-of-band) | ✓ | ✓ | ✓ | ✓ |
| Encryption modes | CFB, CTR, GCM | CFB, CTR, GCM | CFB, CTR, GCM* | CFB, CTR, GCM |
| FPGA based cut-through architecture | ✓ | ✓ | ✓ | ✓ |
| Tamper resistant and evident enclosure | ✓ | ✓ | ✓ | ✓ |
| Anti-probing barriers | ✓ | ✓ | ✓ | ✓ |
| Dual swappable AC or DC power supplies | ✓ | ✓ | ✓ | ✓ |
| User replaceable fans and battery module | ✓ | ✓ | ✓ | ✓ |
| Fully interoperable with related CN/CV models | ✓ | ✓ | ✓ | ✓ |
| Crypto-agile architecture / future quantum-safe roadmap | – | – | – | ✓ |
| Latency – microseconds per encryptor (typical for IPv4 traffic with 64-1518 octet frames) | <10 @ 1Gbps | <5 @ 10Gbps | <5 @ 10Gbps | Ultra-low latency |
| SNMPv1/2 monitoring (read-only) | ✓ | ✓ | ✓ | ✓ |
| NTP (time server) support | ✓ | ✓ | ✓ | ✓ |
| In-field firmware upgrades | ✓ | ✓ | ✓ | ✓ |
Explore the CN6000 Series in detail
Discover the features, specifications and deployment options across the CN6000 Series.


